ICCA: A New Architecture for Privacy in Digital Commerce
Digital commerce has reached a turning point. For more than two decades, online transactions have relied on identity as their foundation. Every purchase, delivery and support interaction has been tied to names, addresses, accounts and behavioural profiles. This model has created convenience, but it has also created risk. Identity exposure, data retention, profiling and breach liability have become structural features of the commercial internet.
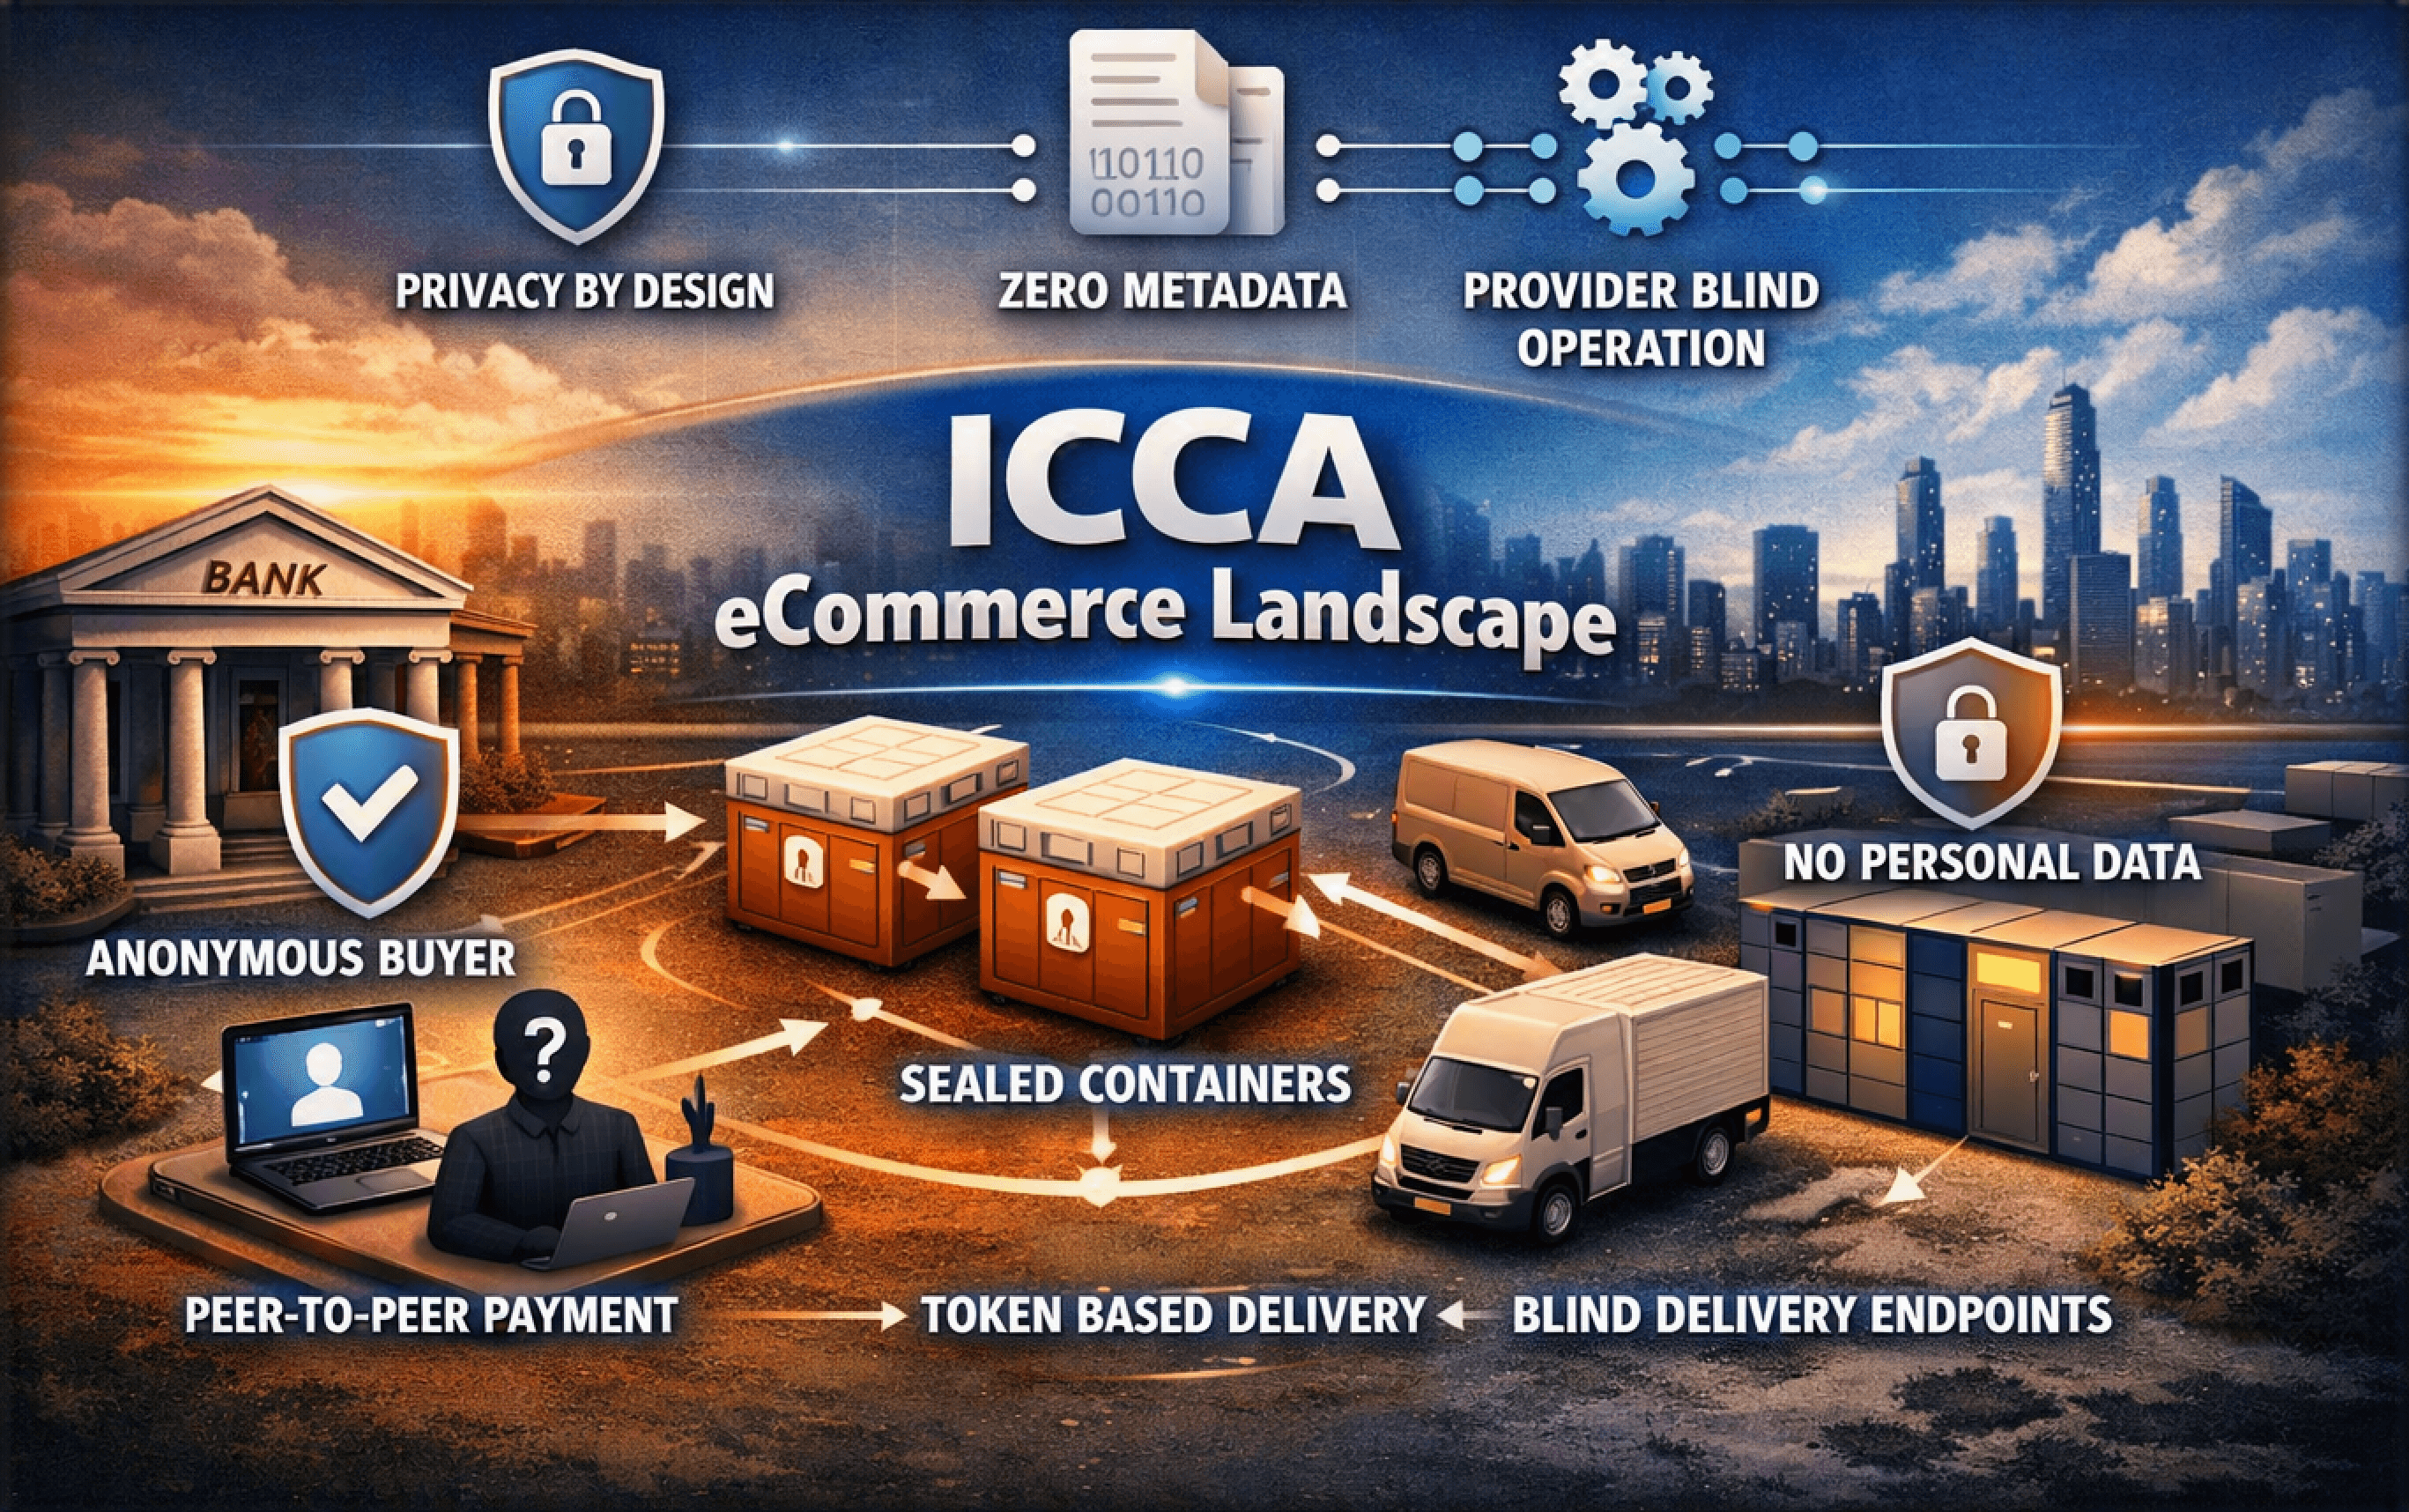
ICCA introduces a different approach. It is a new architectural model that shows commerce can function without identity. ICCA removes personal data from the commercial workflow and replaces it with accountable, non correlatable structures that allow buying, selling and fulfilment to operate without exposing individuals.
This is not a privacy enhancement. It is a redesign of how digital commerce can work.
A new category of digital architecture
ICCA is built on mechanisms that do not exist in traditional eCommerce. These include constructed identity, item containers, blind delivery endpoints, zero metadata transport and envelope based transaction choreography. Each mechanism removes a category of data that commercial systems have historically relied on. Together, they form a trust architecture that operates without identity, without correlatable metadata and without provider visibility.
This creates a new category of digital infrastructure. ICCA is not an extension of account based commerce and not a variation of authentication frameworks. It replaces identity with context bound accountability and replaces metadata with sealed, dissolvable artefacts that cannot be reconstructed.
Why ICCA matters for privacy
Privacy challenges in digital commerce do not come from isolated breaches. They come from structural dependencies. When identity is required for fulfilment, identity must be stored. When metadata is required for routing, metadata must be retained. When accounts are required for support, behavioural profiles must exist.
ICCA removes these dependencies entirely. Sellers operate without identity liability. Delivery agents fulfil items without visibility into personal data. Buyers retain full consumer rights without exposing themselves. The system becomes safer because the data that causes harm is no longer part of the process.
This is privacy through architectural removal, not privacy through policy.
Why ICCA matters for industry
Companies face rising operational costs from identity management, compliance obligations and breach mitigation. They maintain customer databases, secure personal information and respond to regulatory requirements that grow more complex each year.
ICCA offers a simpler model. Sellers operate without identity databases. Delivery partners receive only logistical coordinates. Support teams work with item containers instead of accounts. Compliance becomes easier because the system no longer stores the categories of data that regulations are designed to protect.
Why ICCA matters for regulators
Regulators increasingly emphasise data minimisation, breach liability and identity protection. ICCA aligns with these requirements by relocating identity verification to the banking plane. Banks verify identity for payment approval, but this identity never enters the commerce system. Accountability is maintained through item containers rather than personal data.
This separation satisfies legal obligations while protecting users.
Why self publishing was necessary
ICCA does not fit into existing commercial or academic categories. It is not derived from identity based systems and not built on prior authentication models. Because of this, traditional publishing channels often attempt to frame ICCA within legacy assumptions.
Self publishing through the Omega Foundation ensures that the architecture is presented accurately and without distortion. It allows the work to be shared openly with researchers, regulators and industry leaders who are exploring the future of privacy centric digital ecosystems.
A new direction for digital commerce
ICCA shows that trust does not require identity. It shows that privacy can be protected without reducing functionality. And it shows that digital commerce can be redesigned from first principles to serve people rather than expose them.
This is the beginning of a new category of digital infrastructure. The Omega Foundation will continue to publish research and guidance to support companies, regulators and technologists who want to move beyond identity centric commerce and toward a safer, simpler and more privacy aligned future.
Read the Full Paper on the Omega Foundation
ICCA a Trustless Model for Provider Blind eCommerce by Karl A. L. Smith