Skip to content

Karl A L Smith

Knowledge Should Be Open. Private Data Must Be Protected.

  • Home
  • About Karl
    • ICCA Paradigm
    • Founder
    • Karl A L Smith CV with Addendum
    • Legacy Professional Biography
    • Speaking
    • Recent Interviews
    • Recognition
    • Thought Leader
  • Consulting Services
    • AI Organisational Design
    • All me
    • All me Dev Blog
  • Community Projects
    • Agile World Broadcast Network
  • Travel & Restaurants
  • Contact
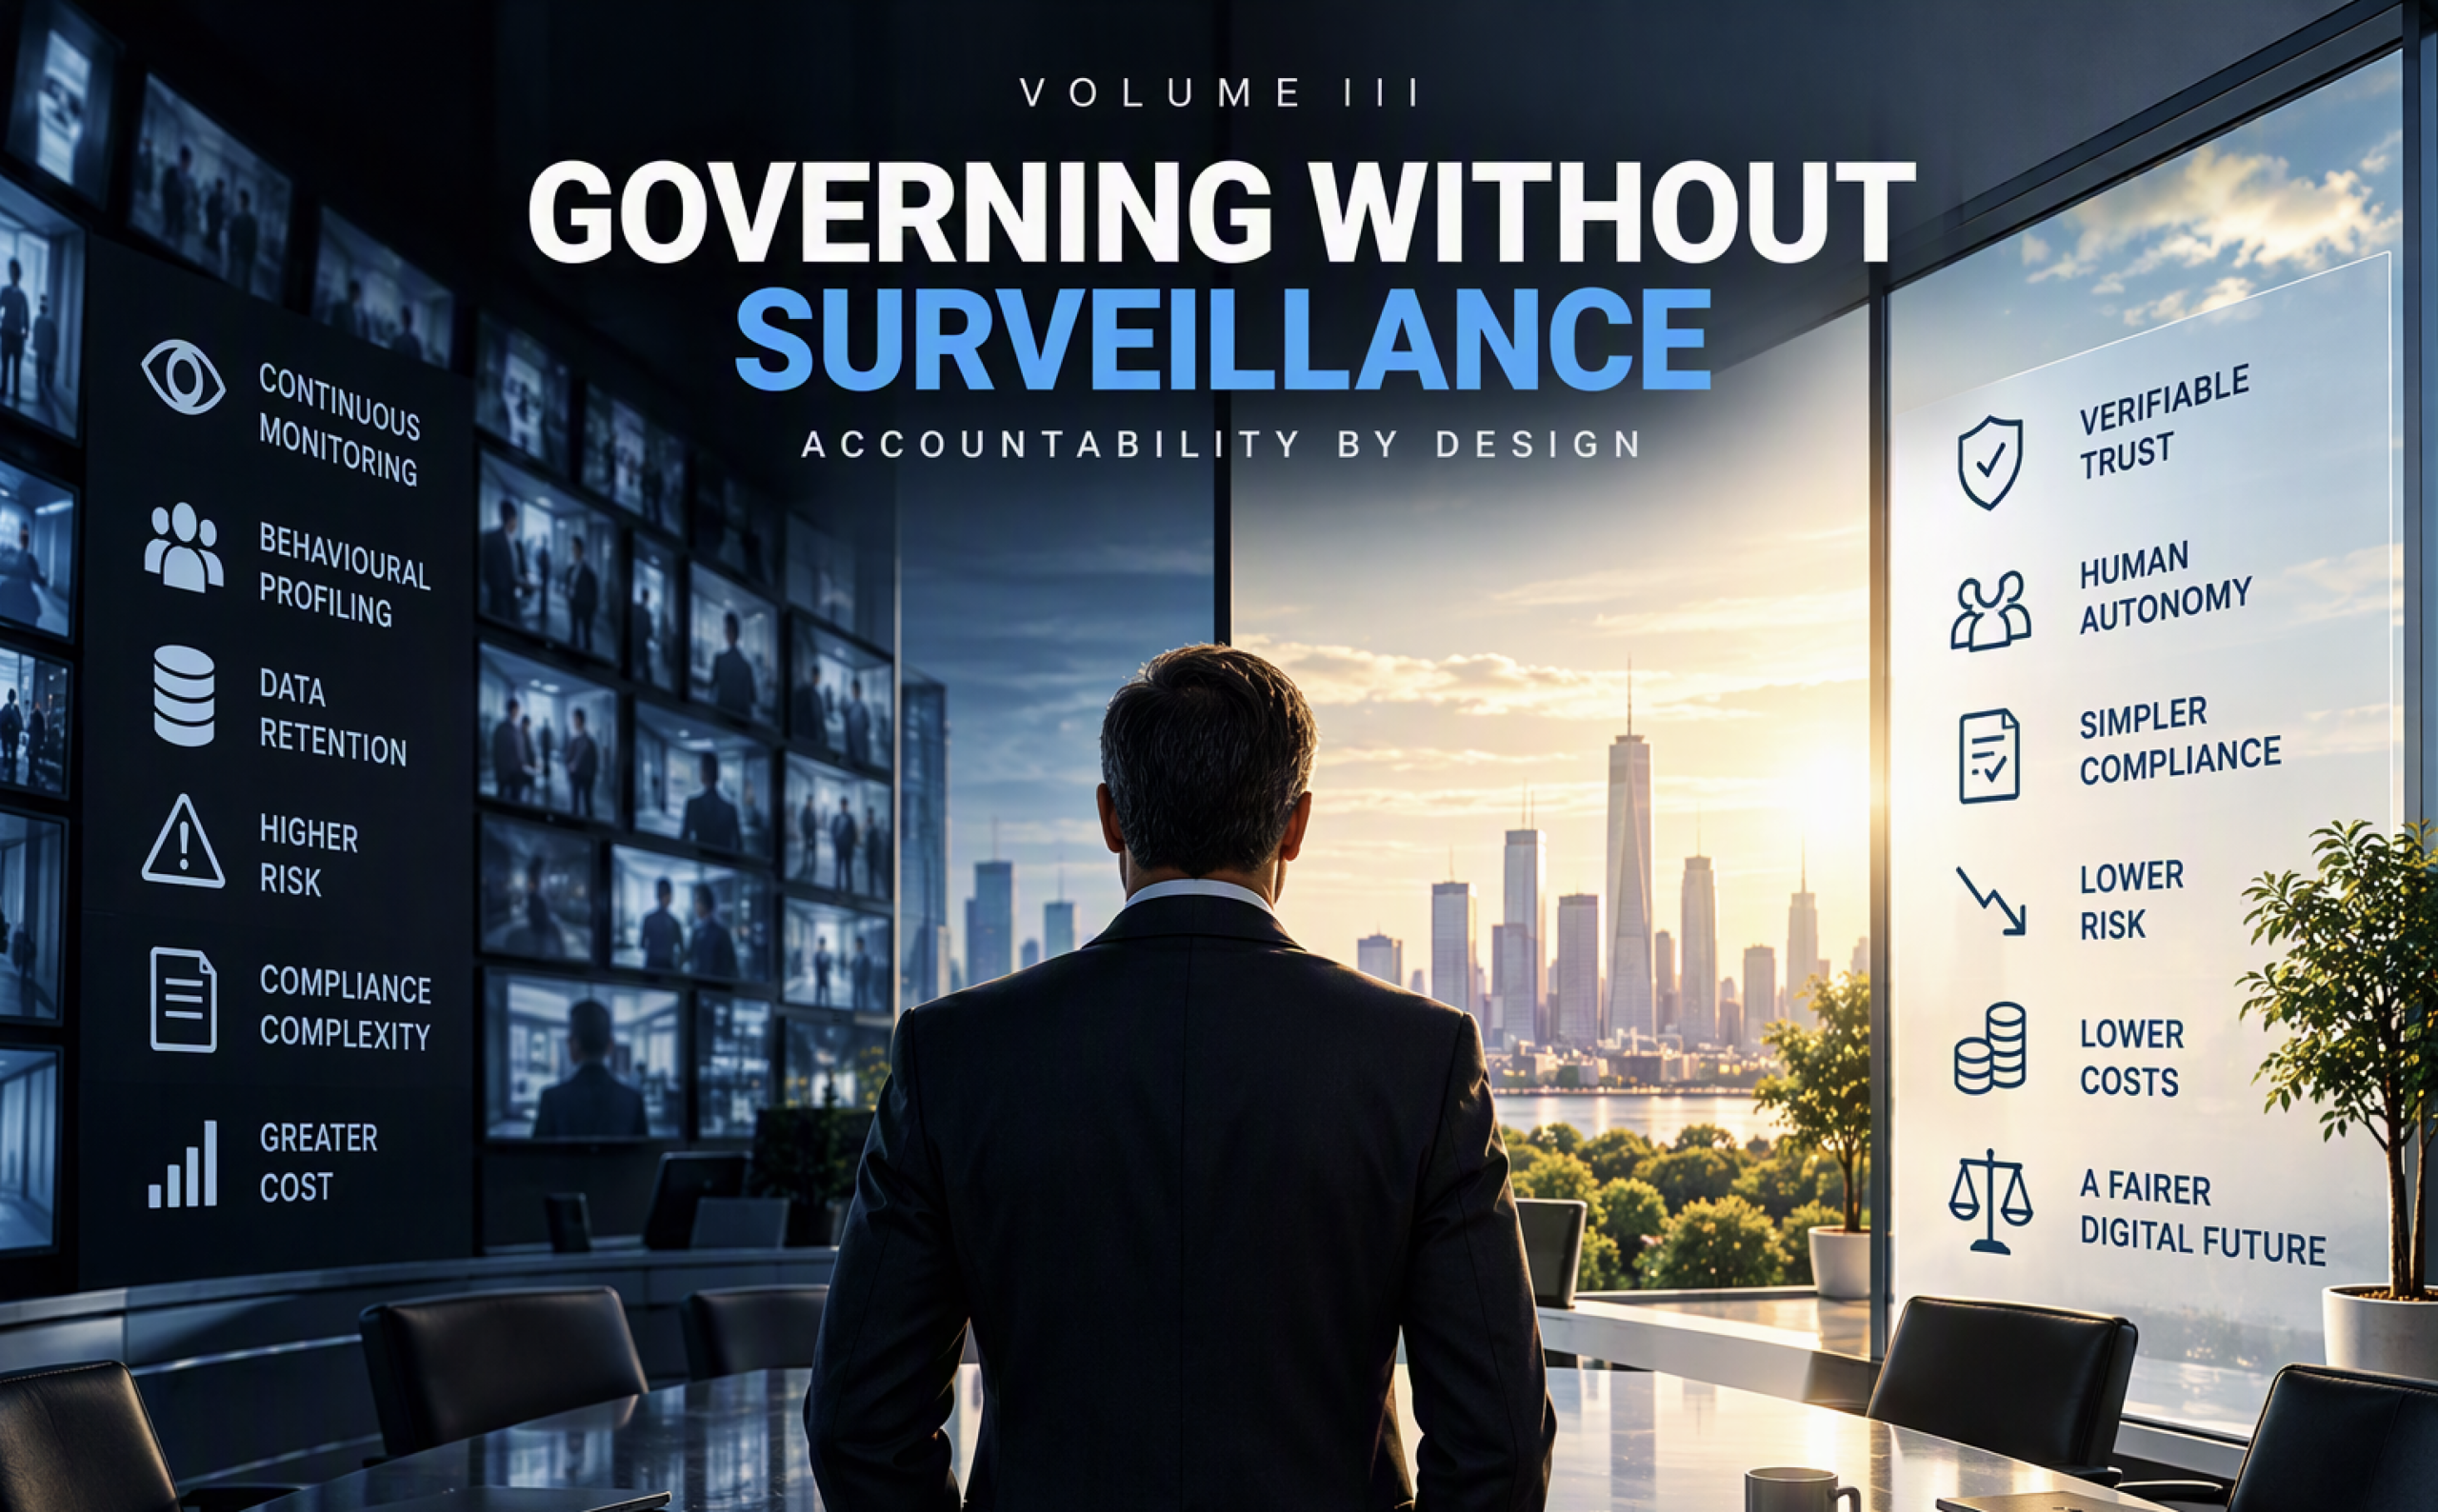
Governing Without Surveillance
 Posted in All me app, Press Release

Governing Without Surveillance

 admin  October 23, 2026

Modern organisations have built much of their governance around visibility.

  • We monitor activity.
  • We maintain records.
  • We analyse behaviour.
  • We create audit trails.

We use information to identify risk, demonstrate compliance and provide organisational oversight.

This has created a deeply embedded assumption:

To govern effectively, an organisation needs to see what is happening.

Volume III challenges that assumption.

It asks what happens to enterprise risk, governance, compliance and accountability when observing the individual is no longer the foundation of organisational control.

For leaders considering a greenfield organisation or platform, this creates an opportunity to design governance alongside the architecture from the beginning.

Instead of collecting extensive information and then creating controls around who can access it, how it can be used, and how long it can be retained, leaders can start with a different question:

What evidence does the organisation actually need to establish that something is legitimate, compliant or authorised?

That distinction matters.

Knowing that something is valid does not necessarily require knowing everything about the person or activity behind it.

For existing organisations

The opportunity is different, and potentially more challenging.

Established governance models may depend heavily on visibility, monitoring, data retention and behavioural analysis.

Volume III provides leaders with a framework for questioning those dependencies.

Where is visibility genuinely necessary for accountability?

Where could a right, authority or obligation be validated without exposing everything around it?

And where has monitoring become synonymous with governance simply because existing technologies made monitoring possible?

This is not an argument for removing accountability.

Quite the opposite.

It asks whether accountability can be made stronger by proving what matters without accumulating information that does not.

A different enterprise risk model

Reducing visibility changes the nature of organisational risk.

Information an organisation cannot see cannot become part of a behavioural profile.

Information it does not retain does not require the same forms of protection and governance.

Information that does not accumulate cannot create the same continuity of exposure.

That means provider blindness should not be considered solely as a privacy proposition.

It potentially changes the economics and structure of risk, compliance, governance and institutional responsibility.

The executive challenge therefore becomes:

Can we preserve accountability without building the organisation around observation?

That is the adoption question at the heart of Volume III.

It moves the conversation beyond protecting individuals from unnecessary visibility and asks something larger:

What would enterprise governance look like if trust came from verifiable constraints rather than continuous observation?

Volume III explores that possibility from the perspectives of enterprise risk, law, governance and organisational design.

The underlying ICCA papers are openly shared under a Creative Commons Attribution-ShareAlike 4.0 licence, allowing the principles to be examined, challenged, adapted and developed beyond All Me.

These articles ask questions that matter to everyday users, business leaders, regulators and policymakers:

  • Do We Really Need to See Everything to Manage Risk?
  • Does Organisational Control Really Require More Oversight?
  • Does Accountability Require Everyone to See Everything?
Total Page Visits: 1109 - Today Page Visits: 1
Author: admin
Tagged Accountability by Design, Accountability Without Surveillance, All me, Architectural Governance, Behavioural Privacy, Blind Provider Architecture, Compliance Without Surveillance, Control Without Visibility, Cryptographic Trust, Cybersecurity Governance, Data Governance, Data Minimisation, Data Privacy, digital autonomy, Digital Governance, Digital Privacy, digital rights, Digital Sovereignty, Digital Trust, ethical technology, Future of Digital Governance, Governance by Design, Governance Without Surveillance, Governing Without Surveillance, Human Autonomy, Human Rights, ICCA, Identity Architecture, identity constructed channels, identity constructed communication architecture, Identity Containers, Information Governance, Metadata Privacy, non inferential systems, organisational governance, Permissioned Interaction, Privacy by Architecture, Privacy by design, Privacy First Technology, Privacy Preserving Governance, Provider Blind Systems, provider blindness, Responsible Technology, Structural Governance, structural privacy, Surveillance Free Governance, Surveillance Free Systems, trust boundaries, Trust Without Visibility, trustless architecture, User Autonomy, Zero Knowledge Architecture, Zero Metadata, zero?metadata transport

Post navigation

Does Accountability Require Everyone to See Everything? →
← What If My Customer’s Behaviour Wasn’t Part of My Business Model

Copyright © 2026 Karl A L Smith

Design by ThemesDNA.com

Manage Consent
To provide the best experiences, we use technologies like cookies to store and/or access device information. Consenting to these technologies will allow us to process data such as browsing behavior or unique IDs on this site. Not consenting or withdrawing consent, may adversely affect certain features and functions.
Functional Always active
The technical storage or access is strictly necessary for the legitimate purpose of enabling the use of a specific service explicitly requested by the subscriber or user, or for the sole purpose of carrying out the transmission of a communication over an electronic communications network.
Preferences
The technical storage or access is necessary for the legitimate purpose of storing preferences that are not requested by the subscriber or user.
Statistics
The technical storage or access that is used exclusively for statistical purposes. The technical storage or access that is used exclusively for anonymous statistical purposes. Without a subpoena, voluntary compliance on the part of your Internet Service Provider, or additional records from a third party, information stored or retrieved for this purpose alone cannot usually be used to identify you.
Marketing
The technical storage or access is required to create user profiles to send advertising, or to track the user on a website or across several websites for similar marketing purposes.
  • Manage options
  • Manage services
  • Manage {vendor_count} vendors
  • Read more about these purposes
View preferences
  • {title}
  • {title}
  • {title}

Privacy Policy