Does Organisational Control Really Require More Oversight?
Most organisations respond to complexity in familiar ways. More reporting. More approvals. More controls. More governance. More management visibility. When something goes wrong, the instinct is often to increase oversight. It seems logical: If leaders can see more of what…
Do We Really Need to See Everything to Manage Risk?
Risk management has traditionally depended on information. Collect more. Monitor more. Retain more. Analyse more. Identify patterns. Spot anomalies. Create audit trails. The logic seems obvious: The more an organisation can see, the better equipped it is to manage risk….
Why Do We Assume Organisations Need To See Everything?
Modern organisations are built around visibility. We monitor. We analyse. We track. We measure. We justify these activities as necessary for security, compliance, operations and customer service. But what if we’ve mistaken visibility for necessity? For decades, digital systems have…
Why Does Every Digital Interaction Leave a Trail?
Every time we interact online, a record is created. A login. A purchase. A search. A message. A click. Most of us accept this as a normal part of digital life. But why? Why should every interaction generate a permanent…
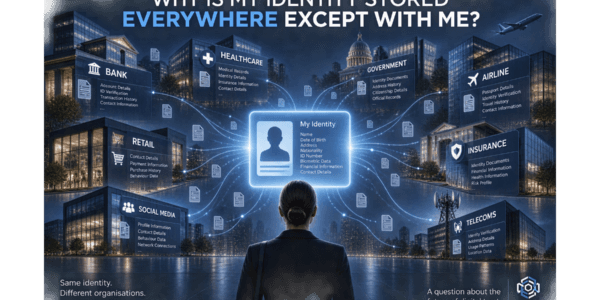
Why Is My Identity Stored Everywhere Except With Me?
Every few weeks another organisation asks me to prove who I am. My bank knows. My employer knows. My insurer knows. My airline knows. Government departments know. Countless websites know. The obvious question is: Why is my identity stored in…
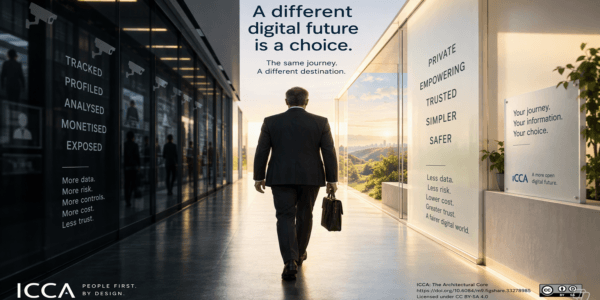
Why Am I Expected to Trust Everyone?
Every person knows this feeling. You book a holiday. You open a bank account. You use a mobile app. You join a loyalty programme. You visit a website. Each interaction comes with an invisible transaction. Your information in exchange for…
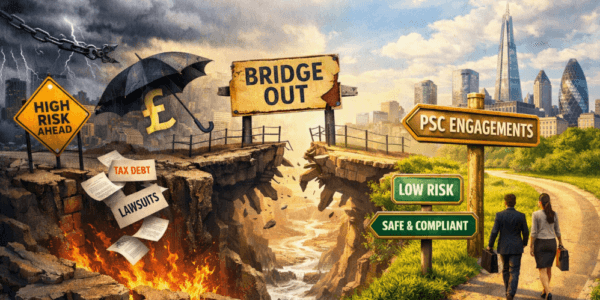
From Umbrellas to PSCs Navigating the UK’s New Contractor Risk Landscape
The UK contingent labour market is undergoing its most significant transformation in two decades. Two legislative changes the Employment Rights Act reforms and the new Joint & Several Liability rules under Chapter 11 ITEPA 2003 are reshaping how businesses engage…

AI Governance Is Failing Because It Eliminates Opportunity: Why deterministic controls cannot deliver outcome-optimising decision-making
Why deterministic controls cannot deliver outcome-optimising decision-making Across industries, AI governance has become a priority. Boards are demanding clarity, regulators are tightening expectations, and organisations are racing to demonstrate responsible AI practices. Yet beneath the surface, a structural flaw is…

Daily P&L for Finance Risk and London Markets
Some people may be astonished to know that daily profit and loss (P&L) exists let alone the capability to delivery it across multiple separate organisations and entities in an enterprise in a 15 minute increment. Some might ask why would…

Silverlight ends in 2021 but Banks still selecting it
I remember being in the discussion at a state owned investment bank when the discussion was being had about which front-end language should be used on their new system interfaces and they choose Silverlight. This choice was known with the…

Banking Change Management through HCD
Massive change management is taking place across all sectors of British banking over the last three years driven by buy outs and mergers, some by efficiencies and a little more recently through questioning the nature and controls around risk management.