Why Is My Identity Stored Everywhere Except With Me?
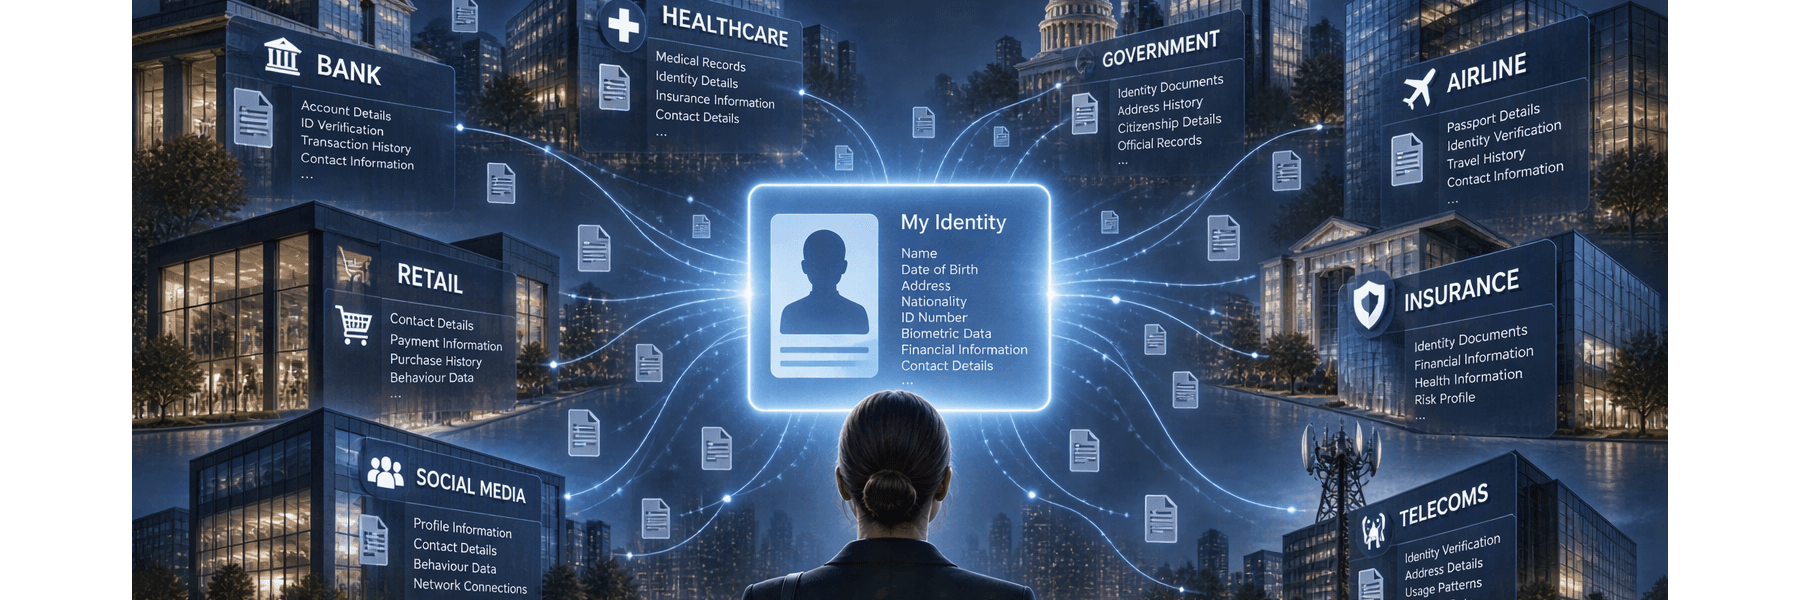
Every few weeks another organisation asks me to prove who I am.
- My bank knows.
- My employer knows.
- My insurer knows.
- My airline knows.
- Government departments know.
- Countless websites know.
The obvious question is:
Why is my identity stored in so many places?
For decades we have accepted a simple assumption.
If an organisation needs to know who I am today, then it must continue holding information about me tomorrow.
That assumption has shaped almost every digital service we use.
The result?
- More databases.
- More copies.
- More verification processes.
- More risks.
- More opportunities for information to be exposed, misplaced or stolen.
But what if we have been solving the wrong problem?
What if proving identity and storing identity are not the same thing?
The second ICCA paper explores this question from an adoption perspective.
Not by asking how organisations can better manage identity.
But by asking whether identity should be distributed across hundreds of organisations at all.
Imagine a world where identity remains with the individual.
Where organisations receive proof when needed.
But do not become permanent custodians of personal information.
The implications extend well beyond privacy.
They influence:
- Risk management
- Cybersecurity
- Regulatory exposure
- Customer trust
- Digital operating models
For greenfield services, this approach could reduce the burden of storing and protecting information that may not be required.
For established organisations, it raises a more strategic question:
How much of our current identity infrastructure exists because it is necessary, and how much exists because it is inherited?
As digital ecosystems become increasingly dependent on identity, this feels like a conversation worth having.
The underlying paper, ICCA Identity Geometry and Data Architecture, is published under the Creative Commons Attribution-ShareAlike 4.0 licence to encourage discussion, challenge, adaptation and further development.
Question for leaders:
If your organisation could verify customers without permanently holding their identity information, would you choose that model?
#ICCA #DigitalIdentity #Leadership #RiskManagement #CyberSecurity #DigitalTransformation #Privacy #Innovation #Governance #CreativeCommons